The task
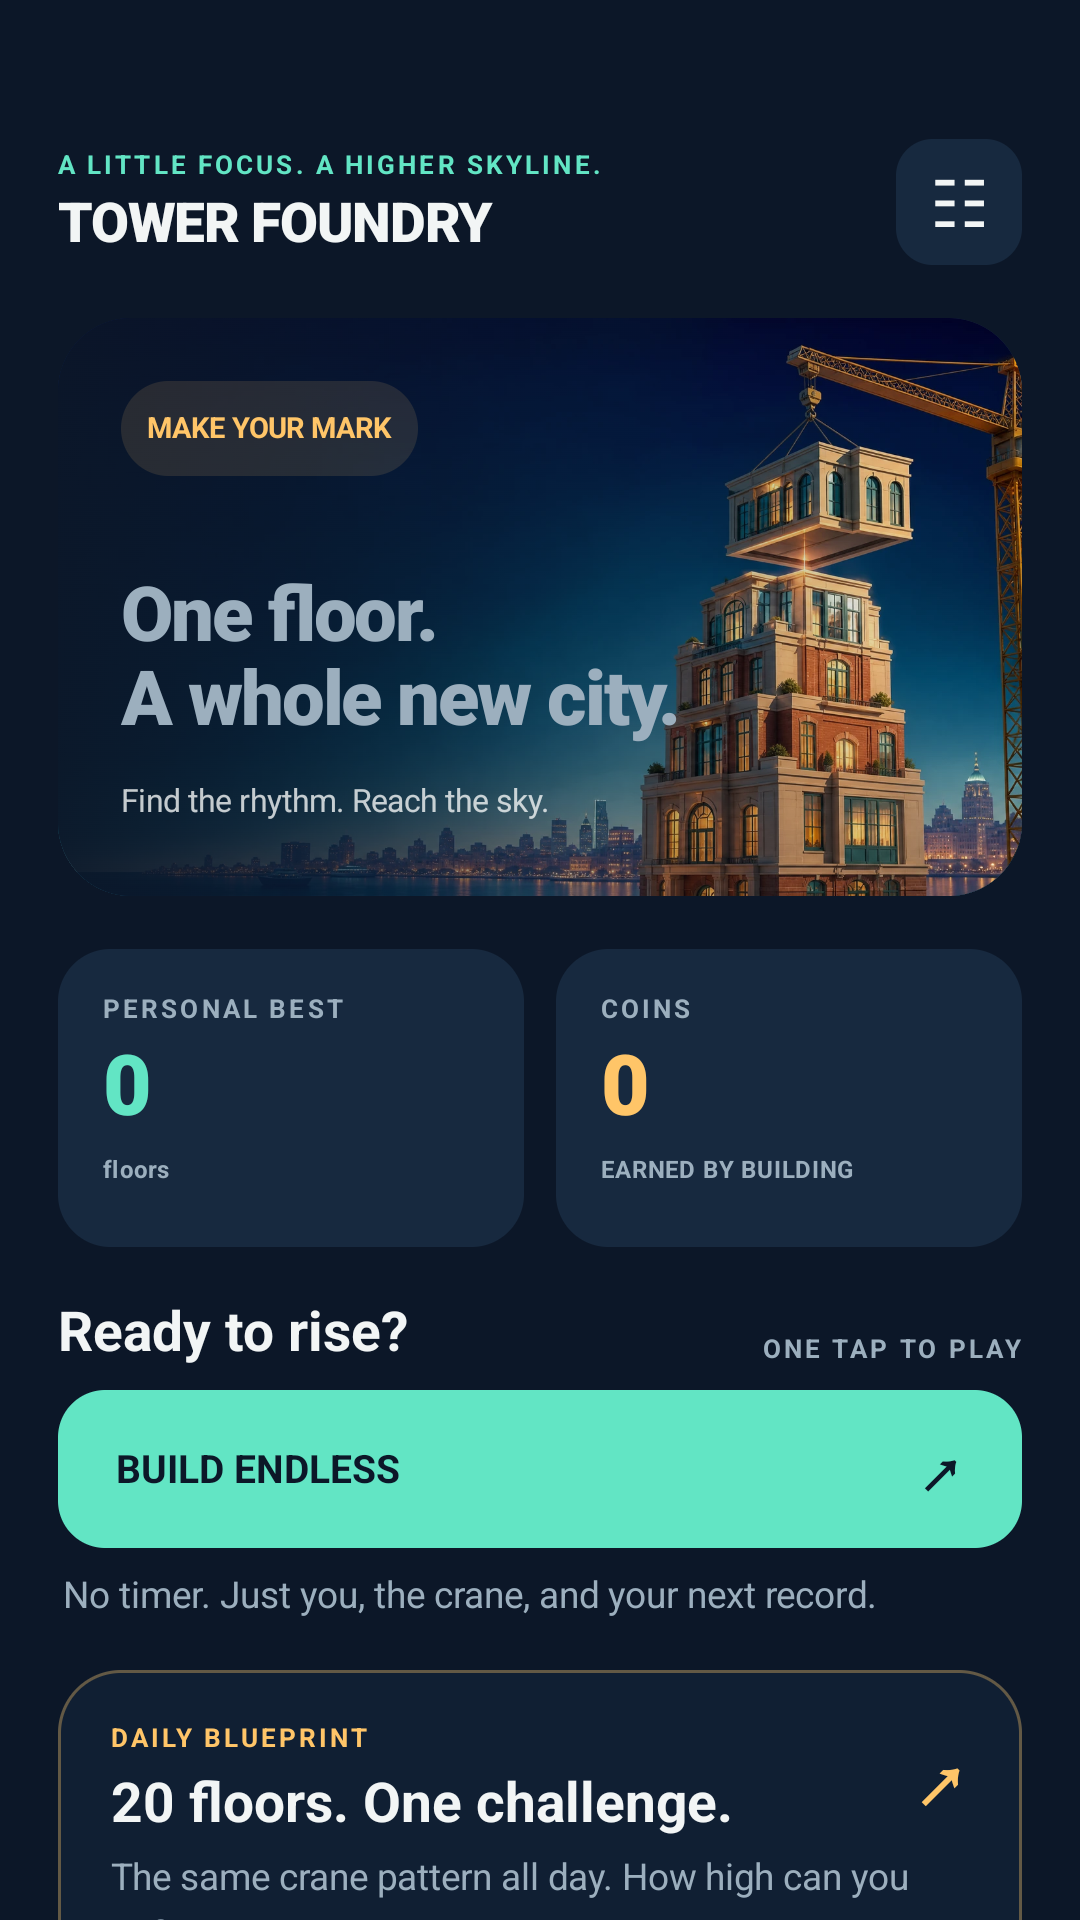
The app combines a local mini-game with a web section. The game stores progress on the device; the embedded browser opens a web product, follows navigation and requests access to device features.
The work includes the details people encounter after installation: Back navigation, file selection, downloads, rotation, activity recreation and a useful network-error screen.
What I implemented
- Native Kotlin screens and game logic, saved progress, onboarding, sound and haptics.
- A WebView with navigation history, popups, fullscreen video and a return path to the native screen.
- File selection and downloads through Android system dialogs; separate permission requests for camera and microphone.
- Confirmation for external links and an explicit error state when a TLS check fails.
- Browser history and screen-state restoration during normal activity recreation.
- Separate Debug and Release variants, external private build settings and R8 release shrinking.
Compilation and decompilation
I use Gradle to produce installable APKs and AABs for publication. For each artifact I check the package ID, version, permissions, resources and signature.
My APK-analysis work includes inspecting the manifest, resources, included libraries and interface behaviour. Partial analysis helped specify the required behaviour for a new implementation in my own app.
The source that can be recovered depends on the language, obfuscation and build contents. I assess the actual artifact and available source before estimating recovery work. I analyse my own apps or work with the rights holder’s permission.
Verification
The projects include automated tests for game logic, navigation policies, analytics consent and event queues. Release candidates have saved build, lint, signature and emulator checks.
File selection, permissions, browser restoration, offline states and certificate errors have separate scenarios. A version and APK checksum identify the exact candidate used in a check.
Result and scope
The work produced own source projects, working app builds and a repeatable preparation and verification process. I use that experience to build Android apps, add a web section and maintain existing projects.
This case covers development and build verification. Store acceptance and external-service behaviour are checked separately for each app. Sales growth and install counts were not measured in this project.